New: AI Workspace – Secure AI for Organizations With Sensitive Data. Learn more.


What is the EU Cloud Sovereignty Framework?
The EU Cloud Sovereignty Framework is a reference framework developed by the European Commission that enables companies and public authorities to systematically assess the digital sovereignty of cloud services. Among other things, it describes requirements for data locations, legal control over data access, and the technological and operational independence of cloud providers. This transforms the abstract concept of “cloud sovereignty” into a concrete, measurable criterion that can serve as a basis for strategic decisions and tenders.
Eight clearly defined sovereignty objectives, for example for strategy, law, data, technology, and operations.
Five-level assessment model (SEAL) to classify the level of sovereignty achieved by a provider.
Decision-making aid for selecting cloud services that meet EU requirements for data protection, security, and digital sovereignty.


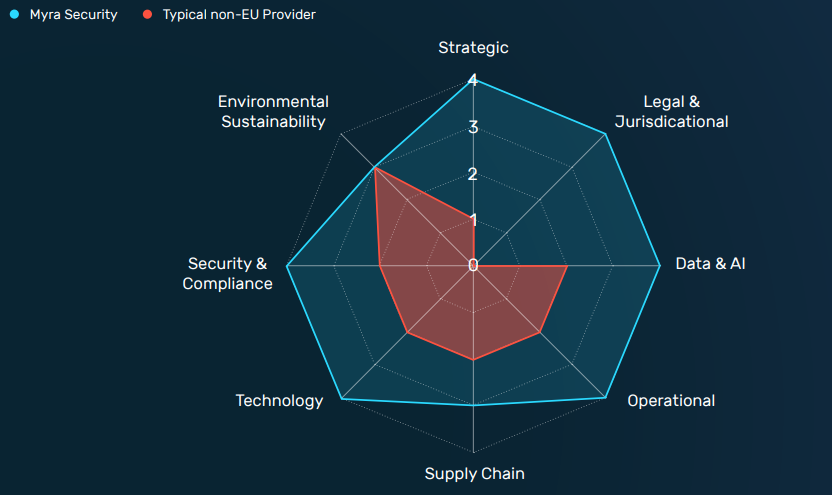
For providers outside the European Union, some of the criteria required by the Cloud Sovereignty Framework are simply impossible to meet—particularly with regard to legal and jurisdictional sovereignty.


Where Myra sets itself apart from non-EU providers
(Download the report now for the entire table.)
Strategic Sovereignty (SOV-1)
Myra is an owner-managed company with exclusively European shareholders from the DACH region
Headquarters and seat of the entire management in Germany
No critical dependencies on customers or partners outside the EU
Development and operation of the protection services are carried out independently from Germany on our own hardware, independently of service providers
Legal & Jurisdictional Sovereignty (SOV-2)
Myra is subject solely to German and European law
No possibility for non-EU authorities to force access to data or systems
No risk of usage restrictions due to international regulations
Creation of intellectual property, development, and operation exclusively in Germany in accordance with EU law
How you can benefit from digitally confident cybersecurity with Myra


Reliable cyber resilience
Fail-safe availability and data security in accordance with European laws and values – without risks from political influence or foreign law


Preservation of data sovereignty
Compliance with EU data protection standards builds trust and protects both customer and business data, for example thanks to GDPR-compliant TLS termination.


Less regulatory effort
More efficient implementation and verifiable compliance with national or European cybersecurity requirements such as NIS-2, DORA, or the Cyber Resilience Act (CRA)


Robust supply chain
No abrupt price increases or access restrictions due to tariff wars, trade barriers, or other geopolitical developments