update page now

New: EU CAPTCHA – GDPR-compliant bot protection. Try it free for 3 months!

Made in Germany

Network DDoS Protection (cloud)

  • Secure your data centers against volumetric attacks with DDoS scrubbing

  • Prevent costly downtime due to overload attacks

  • Legally GDPR-compliant and made in Germany

Comprehensively certified|Regularly audited|Legally GDPR-compliant

Top-Class DDoS Scrubbing, Tailored to Your Needs

Instant and Reliable DDoS Attack Defense

Top-tier DDoS protection—regardless of your infrastructure, with no vendor lock-in, and up and running in minutes.

  • Comprehensive protection at the network and protocol levels: SYN floods, UDP amplification, DNS reflection, and many other attacks are reliably blocked—starting at IPv4 /24 and IPv6 /48.

  • Quick to implement:No additional hardware or software required. Integration and configuration in just a few steps.

  • Transparent defense provided by the Myra SOC:Immediate notification of attacks and a detailed incident report within 48 hours (on business days).

Full Flexibility in Setup and Operation

Two operating modes, seamless integration – adapts to your needs.

  • On-demand or Always-on: On-demand analyzes real-time traffic and initiates mitigation fully automatically within seconds. Always-on routes all traffic through the Myra infrastructure – for maximum response speed.

  • Flexible connectivity: Connect via Direct Connect, GRE tunnels, VLAN, or IPsec – regardless of your infrastructure.

  • Minimal configuration, maximum protection: Myra monitors traffic flows in real time and automatically initiates mitigation in the event of suspicious anomalies. The Myra SOC provides manual optimizations as needed.

Our key benefits at a glance

This Is Why CISOs Choose Myra

Icon certified and audited

Unlock the Power of Our Comprehensive Certification

Experience peace of mind knowing that our cutting-edge technologies, exceptional services, and streamlined processes are meticulously audited and certified to surpass the highest industry standards.

Icon Made in Germany

Embrace Quality with Our "Made in Germany" Assurance

As a company based in Germany, we strictly adhere to the stringent regulations imposed by the GDPR, ensuring that your data privacy is our top priority.

Icon Support

Experience Unmatched Support, Anytime, Anywhere!

Receive unparalleled assistance from a team of security experts, part of our reputable Myra Security Operations Center. We're available 24/7 to address any concerns and provide you with guidance.

Certified Security You Can Rely On

Certificate ISO 27001 BSI certified on the basis of IT-GrundschutzCertificate PCI DSSISO 9001BSI C5 Testat Typ2Zertifikat Trusted CloudIDW WPS 951 Type 2 CertificateKRITIS LogoBSIG KRITIS qualified logo
Network DDoS Protection (cloud)

Key Features at a Glance

Myra Security Career Icon Compliance Management

Security for Critical Infrastructure

Highly efficient DDoS protection for mitigating a wide range of attack vectors.

Icon Protect Webservices

On-demand Operation

Fully automated mitigation with switchover times of a few seconds in the event of an attack.

Flow Monitoring

Real-time traffic analysis in own data center for individual mitigation configuration.

Icon WebTech

API

Optional automated or manual switching of subnets via API call.

Icon Online Protection

IPv4 und IPv6

Protection for IP subnets from /24 for IPv4 and /48 for IPv6.

GRE

Universal traffic forwarding via GRE tunnel.

Icon traffic filter

VLAN

High-performance and flexibly configurable connection for the transmission of clean traffic.

Direct Connect

The direct connection between your infrastructure and Myra makes you independent of disturbances in the public network.

IPsec (optional)

Encrypted forwarding of clean traffic for increased security requirements.

Provider independence

Myra Network DDoS Protection (cloud) can be implemented quickly and independently of existing infrastructure and providers.

Comprehensive Peering Options

Connection of your infrastructure to the most important data centers and Internet nodes.

Icon Attention Report

Reporting

Incident reports from the Myra SOC with detailed information about incidents.

You're in Good Company When You Choose Myra

1&1 VersatelLogo BarmeniaMunich Security ConferenceSparkasse LogoEdekadpallb1861 LogoLogo of Aleph Alpha, German AI company and customer of Myra SecurityCancomPartner of Myra: WitcomPartner of Myra: heinleinLogo Staatsministerium Baden-WürttembergStadt Regensburg LogoSecuritas1822direkt LogoHugendubel Logokik LogoBreuninger LogoAKDB LogoLogo of KDVZ, German municipal IT service provider and customer of Myra Security

Know-How and Support Are Crucial for DDoS Protection

Myra provides fast, uncomplicated and reliable help - whether via emergency onboarding in the event of an imminent cyberattack or with preventive measures. Our flexible solutions can be implemented at short notice, as they do not require any additional hardware or software.

The expert team at the Myra Security Operations Center (SOC) provides support in setting up, configuring and operating our services. In addition, the Myra SOC is available 24/7 to provide our customers with advice and assistance in defending against attacks.

These Attacks Threaten Your IT Infrastructure

All attacks on the network and transport layer (layers 3 and 4) overload the target with very high bandwidths or immense packet rates. This means that legitimate attempts to access the data channel to establish communication are no longer possible.

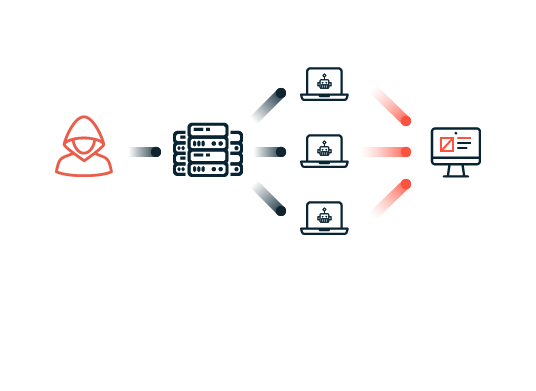
In a SYN-ACK flood attack (or SYN and ACK floods), for example, a botnet remotely controlled by attackers bombards a server with SYN packets. They are usually part of what is called at three-way handshake, which occurs when a TCP connection is established between client and server.

A SYN/ACK attack produces a huge number of half-open connections by sending many SYN, but none of the ACK packets needed to establish a full connection. As a result, no new connections can be established and the website is no longer accessible.

DDoS attacks

How DDoS Scrubbing Protects Your Data Centers

In the event of an attack, all traffic is redirected to the Myra infrastructure via an automatically triggered "more specific BGP announcement". The Myra DDoS scrubbing center filters out the malicious attack traffic and discards it, while the valid clean traffic is still delivered to the target server. This means that there is no additional load on your origin server, even in the event of an ongoing attack.

Once the attack is over, the BGP announcement is withdrawn. The data packets then flow directly to your infrastructure again and there is no more filtering by Myra.

DDoS Protection Layers

Know-How and Support Are Crucial for DDoS Protection

Myra provides fast, uncomplicated and reliable help - whether via emergency onboarding in the event of an imminent cyberattack or with preventive measures. Our flexible solutions can be implemented at short notice, as they do not require any additional hardware or software.

The expert team at the Myra Security Operations Center (SOC) provides support in setting up, configuring and operating our services. In addition, the Myra SOC is available 24/7 to provide our customers with advice and assistance in defending against attacks.

These Attacks Threaten Your IT Infrastructure

All attacks on the network and transport layer (layers 3 and 4) overload the target with very high bandwidths or immense packet rates. This means that legitimate attempts to access the data channel to establish communication are no longer possible.

In a SYN-ACK flood attack (or SYN and ACK floods), for example, a botnet remotely controlled by attackers bombards a server with SYN packets. They are usually part of what is called at three-way handshake, which occurs when a TCP connection is established between client and server.

A SYN/ACK attack produces a huge number of half-open connections by sending many SYN, but none of the ACK packets needed to establish a full connection. As a result, no new connections can be established and the website is no longer accessible.

DDoS attacks

Protect your business now: 
Submit a non-binding price request

Get a Customized Solution That Fits Your Needs.

Myra's automated defenses take effect in less than a second.

Fast Response Icon

Service level agreement (SLA) for availability of up to 99.999%.

SLA Icon

More than 50 Tbps defense capacity for volumetric attacks.

DDoS Schutz Icon

Over 500 companies from highly regulated sectors such as finance, government institutions, healthcare, and critical infrastructure place their trust in us.

"Myra puts us in a solid position in terms of cybersecurity, web-performance and compliance."
Hendrik Hoffmann, Division Manager Technology at Sparkassen-Finanzportal GmbH

Portrait photo of Hendrik Hoffmann

All information on data processing can be found in our privacy policy.

DDoS Scrubbing – Frequently Asked Questions (FAQ)

DDoS scrubbing is used to mitigate distributed denial of service (DDoS) attacks, which aim to cause delays and outages of websites and IT infrastructures via artificial requests. With DDoS scrubbing, the data traffic is redirected to a DDoS scrubbing center in the event of an attack. There, the attack traffic is filtered out and the clean traffic is forwarded to the target server. The redirection to the scrubbing center is usually carried out via DNS for individual services or via BGP for entire IP address ranges.