update page now

New: EU CAPTCHA – GDPR-compliant bot protection. Try it free for 3 months!

IT Security for the Financial Sector

Myra offers customized IT security solutions for the financial sector. With our highly efficient defense systems, we equip institutions against the biggest digital threats. At the same time, Myra's performance solutions ensure that IT security advances banks in their operational business and does not restrict them.

Trusted by CISOs

Finance customers of Myra: flatexDEGIROLLB 1861Finance customer of Myra: DSV IT ServiceFinance customer of Myra: smavaLogo Inn usLogo FinoaFinance customer from Myra: LendicoFinance customer of Myra: auxmoney1822direkt LogoSparkasse Logo
Cybersecurity

How It Security Is Driving Banks Forward

Cyberattacks cause immense costs for affected companies. In extreme cases, inadequate IT security can place an enormous burden on banks and even threaten their very existence. According to a survey by Lünendonk / KPMG, 7 out of 10 IT managers expect their institution to suffer serious damage as a result of DDoS attacks.

Through IT risk management, banks implement effective IT security measures and thus increase their operational resilience. In this way, IT security indirectly contributes to the economic success of an institution.

Person in suit standing on stairs

Critical-Infrastructure-Proven Protection Systems for Banks

Icon DDoS Schutz

DDoS Protection

Myra automatically detects and blocks malicious traffic, keeping your applications available even under heavy DDoS attacks.

Learn more
Icon WAF

Web Application Firewall

The Myra Web Application Firewall detects and blocks suspicious activity in real time, protecting against known exploits and zero-day vulnerabilities.

Mehr erfahren
Icon Global CDN

CDN

With a global network of strategically placed servers, Myra delivers your content fast and with low latency.

Mehr erfahren
Directives and regulations

IT Compliance as a Regulatory Challenge

Especially in the financial industry, the regulatory requirements for digital systems and processes are immense. A high level of expertise and reliable technology is required to ensure that banking IT complies with the requirements of the German Banking Act (KWG), MaRisk, BAIT and DORA. The General Data Protection Regulation (GDPR) and the NIS 2 Directive must also be observed.

Institutions that exceed certain transaction thresholds are classified as critical infrastructures (KRITIS), which are subject to stricter IT risk management requirements. Overall, regulatory guidelines require affected institutions to regularly demonstrate compliance with strict protection guidelines and to ensure the integrity, availability, authenticity, and confidentiality of data and processes.

Exterior view of skyscrapers in banking district
The biggest threats to digital banking

OWASP Top 10

The OWASP Top 10 is a list of the ten most critical security risks for web applications, which is compiled and regularly updated by the Open Web Application Security Project (OWASP) Foundation. They serve as an important document for developers and security experts to find out about the most common and most dangerous security vulnerabilities in web applications.

The biggest threats to digital banking

DDoS Attack

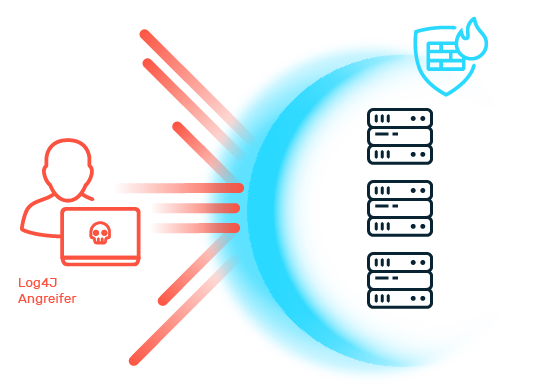
In a distributed denial of service (DDoS) attack, attackers direct artificial traffic to the IT infrastructures, web applications or online APIs of banks and payment service providers. As a result, the affected services are slowed down or fail completely. The problems continue until the attacker ends the attack or the affected institution takes appropriate countermeasures.

DDoS attacks
The biggest threats to digital banking

Credential Stuffing

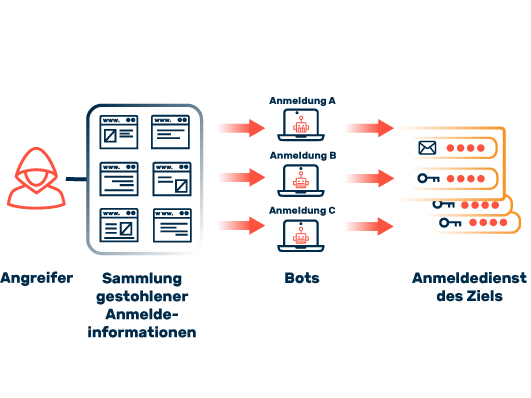
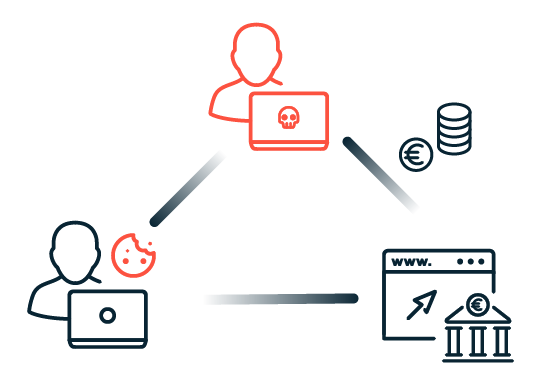
The systematic misuse of access data through credential stuffing is one of the most frequently used methods of attack by cybercriminals against financial services and payment services. Above all, trading the stolen information is a lucrative source of income for attackers.

Sequence of an attack by means of credential stuffing
The biggest threats to digital banking

Cross-Site Scripting (XSS)

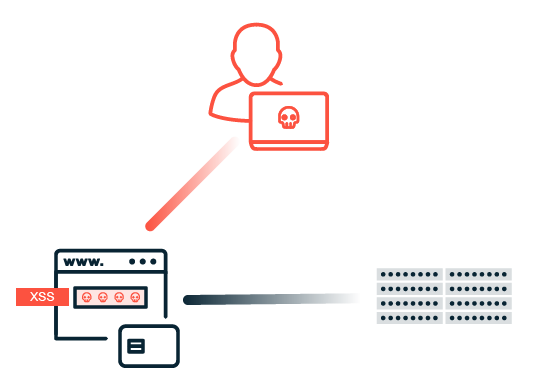
In an XSS attack, cybercriminals inject malicious code into web applications by exploiting security vulnerabilities. XSS attacks allow attackers to gain control of a victim's browser, steal sensitive data such as cookies or login information and potentially compromise the entire user account.

Cross-Site Scripting (XSS)
The biggest threats to digital banking

SQL Injection

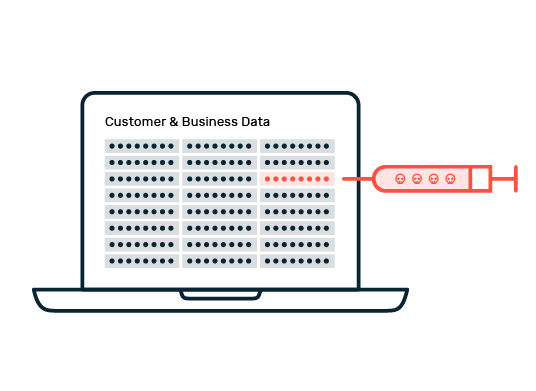
In an SQL injection attack, cybercriminals specifically exploit security vulnerabilities to inject manipulated commands or malicious code via input masks, for example. The attackers aim to manipulate the underlying database and gain unauthorized access to confidential information.

SQL Injection
The biggest threats to digital banking

Zero-Day Exploits

Zero-day exploits are security gaps in software or hardware that are still unknown to the manufacturer and for which there are no patches yet. These vulnerabilities are exploited by attackers to compromise systems, often before the affected companies have even found out about the gap. Nevertheless, there are suitable solutions for taking appropriate countermeasures promptly until the necessary updates are available.

The biggest threats to digital banking

Cross-Site Request Forgery (CSRF)

Attackers trick the user's browser into sending manipulated HTTP requests to a website or web application to trigger unwanted actions. This is done, for example, by sharing manipulated links or by visiting malicious websites, which in turn execute an HTTP request in the context of the existing user session.

Cross-Site Request Forgery (CSRF)
The biggest threats to digital banking

OWASP Top 10

The OWASP Top 10 is a list of the ten most critical security risks for web applications, which is compiled and regularly updated by the Open Web Application Security Project (OWASP) Foundation. They serve as an important document for developers and security experts to find out about the most common and most dangerous security vulnerabilities in web applications.

The biggest threats to digital banking

DDoS Attack

In a distributed denial of service (DDoS) attack, attackers direct artificial traffic to the IT infrastructures, web applications or online APIs of banks and payment service providers. As a result, the affected services are slowed down or fail completely. The problems continue until the attacker ends the attack or the affected institution takes appropriate countermeasures.

DDoS attacks
Sanctions

Fines and Administrative Liabilities

Financial companies that violate the regulatory requirements for data security or data protection face drastic fines of up to 20 million euros (in accordance with the GDPR). NIS-2 and DORA also hold the responsible management bodies accountable. These regulations not only provide for high fines, but also for personal liability of managers if they neglect their duties to ensure data security. In addition to financial sanctions, penalties can include criminal prosecution, increasing the pressure on companies and their executives to implement and continuously monitor stringent security measures.

Person works on two laptops

Fortify Your Digital Defenses With Myra

4 key areas – 1 outstanding technology

Icon radar

Security

Avoid data theft, system outages, and disrupted communications. Our robust defense system protects your critical processes with unwavering vigilance.

Icon Performance

Performance

Experience high-performance delivery of your content, even during traffic peaks. Maintain optimal performance and provide your users with a seamless experience.

Icon Compliance

Business Continuity

Myra ensures the utmost protection for your business by utilizing direct and geo-redundant connections to your infrastructure, without relying on external factors.

Icon Certificate Management

Compliance

Meet the requirements of IT security and data protection teams with ease. Myra is your trusted partner, offering unrivaled expertise in the strictest compliance regimes.

SPARKASSE.DE

Sparkasse Relies on Myra

With our expertise, smart solutions, and successful certifications, we have what it takes to protect customers in the finance sector. With Sparkasse.de, Myra protects, among other things, the central online presence of the Sparkasse. As a German expert in IT security, Myra is the compliance guarantor for essential and non-essential outsourcing.

Sparkasse Building
Designed and engineered for highly regulated sectors

Certified Security from Myra: Compliance Without Compromise

  • ISO 27001 on the basis of IT-Grundschutz (BSI)

  • Payment Card Industry Data Security Standard (PCI DSS)

  • BSI C5 Type 2

  • KRITIS Proof according to § 8a para. 3 BSIG

  • Trusted Cloud Service

  • IDW PS 951 Type 2 (ISAE 3402)

  • VS-NfD

Certificate ISO 27001 BSI certified on the basis of IT-GrundschutzCertificate PCI DSSBSIG KRITIS qualified logoBSI C5 Testat Typ2Zertifikat Trusted CloudIDW WPS 951 Type 2 Certificatebrandeins best IT-security provider 2024 certificate
Case Study

Regulation-compliant IT security for Finoa

Industry: Finance
Number of employees: >50

Myra offers Finoa fully automated protection of its solutions against DDoS attacks, malicious code and bots. Since implementing the Myra solutions, Finoa has benefited from a comprehensive security architecture that reliably protects its platform.

Do you have
questions?

Please contact us via contact form or call us at:
+49 89 414141 - 345.

Alle Informationen zur Datenverarbeitung finden Sie in unseren Datenschutzbestimmungen.

FAQ: Financial Sector and IT Security

DORA (Digital Operational Resilience Act) and NIS-2 (Network and Information Security 2) are two important EU regulations designed to strengthen cybersecurity in the financial sector and other critical infrastructures. DORA aims to ensure the operational resilience of digital systems in the financial sector. It ensures that financial institutions remain operational and financial services remain available even in the event of cyberattacks. NIS-2 harmonizes cybersecurity requirements for critical infrastructure and essential services in the EU. It places particular emphasis on risk management and the reporting of security incidents.