New: AI Workspace – Secure AI for Organizations With Sensitive Data. Learn more.

Cybersecurity for Critical Infrastructures (KRITIS)

Critical infrastructure operators (KRITIS) benefit from Myra's robust protection systems for their sensitive IT landscapes. To this end, Myra designs and implements high-performance security solutions that protect vital infrastructures, harden mission-critical processes against risks, and significantly increase operational efficiency.

Trusted by CISOs

Logo Staatsministerium Baden-WürttembergMunich Security ConferenceG7 Germany1&1 Versatel LogoNFON
IT Security

Why Critical Infrastructures Depend on Cybersecurity

The threat situation for operators of critical infrastructures (KRITIS) has worsened significantly in recent years. It is worrying that three out of four cyberattacks specifically target KRITIS organizations. In the first quarter of 2024, a total of 181 security incidents were reported to the Federal Office for Information Security (BSI). On average, one in six KRITIS organizations was affected by a cyber incident. These figures underline the urgent need to continuously optimize IT security measures and adapt them to new threat scenarios.

For critical infrastructure operators, effective IT security is not only a protective shield, but also a decisive factor for their operational resilience. By implementing comprehensive IT security concepts, critical processes can be maintained and potential outages minimized. This contributes significantly to the stability of the infrastructure and ultimately ensures the reliable supply of vital services to the population.

Airport

Critical-Infrastructure-Proven Protection Systems

Icon DDoS Schutz

DDoS Protection

Myra automatically detects and blocks malicious traffic, keeping your applications available even under heavy DDoS attacks.

Learn more
Icon WAF

Web Application Firewall

The Myra Web Application Firewall detects and blocks suspicious activity in real time, protecting against known exploits and zero-day vulnerabilities.

Mehr erfahren
Icon Global CDN

CDN

With a global network of strategically placed servers, Myra delivers your content fast and with low latency.

Mehr erfahren
Regulatory

Compliance Requirement: Cybersecurity at the Highest Level

The compliance requirements for digital systems and processes for operators of critical infrastructures are particularly extensive. A high level of expertise, reliable technologies and experienced partners are required to secure the IT systems of critical infrastructure facilities in accordance with the requirements of the IT Security Act, the CRITIS Regulation and, in particular, the NIS 2 Directive.

The NIS 2 Directive aims to ensure a high common level of cybersecurity in the EU and strengthen the resilience of critical sectors. It extends the scope to additional sectors, tightens security requirements and introduces stricter enforcement measures to improve cybersecurity across the EU.

Digital threats for operators of critical infrastructures

OWASP Top 10

The OWASP Top 10 is a list of the ten most critical security risks for web applications, which is compiled and regularly updated by the Open Web Application Security Project (OWASP) Foundation. They serve as an important document for developers and security experts to find out about the most common and most dangerous security vulnerabilities in web applications.

Digital threats for operators of critical infrastructures

DDoS Attack

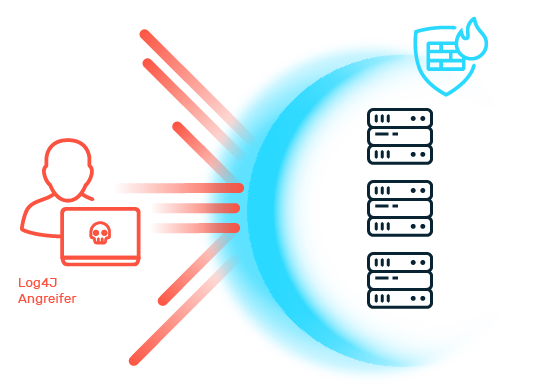
In a distributed denial of service (DDoS) attack, attackers direct artificial traffic to the IT infrastructures, web applications or online APIs of operators of critical infrastructures. As a result, the affected services are slowed down or fail completely. The problems continue until the attacker ends the attack or the affected organization takes appropriate countermeasures.

DDoS attacks
Digital threats for operators of critical infrastructures

Credential Stuffing

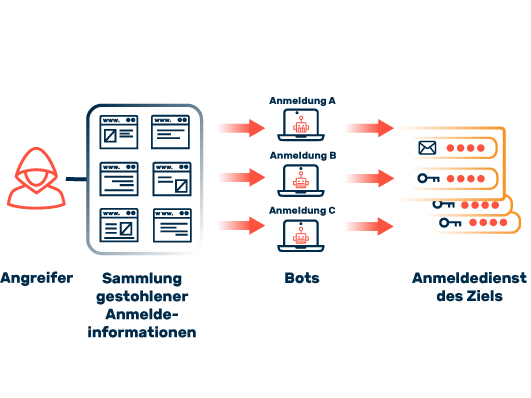
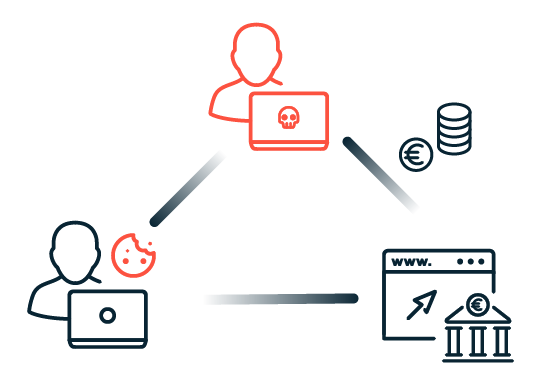
The systematic misuse of access data through credential stuffing is one of the most frequently used methods of attack by cybercriminals against operators of critical infrastructures. Above all, trading the stolen information is a lucrative source of income for attackers.

Sequence of an attack by means of credential stuffing
Digital threats for operators of critical infrastructures

Cross-Site Scripting (XSS)

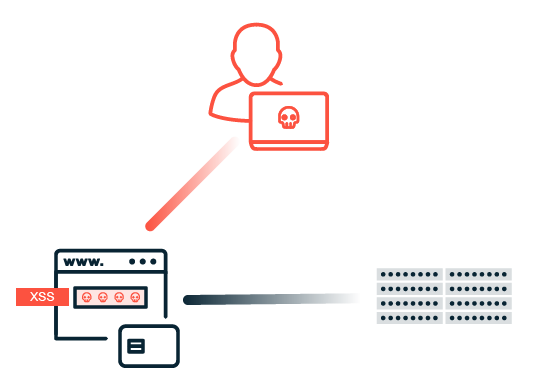
In an XSS attack, cybercriminals inject malicious code into web applications by exploiting security vulnerabilities. XSS attacks allow attackers to gain control of a victim's browser, steal sensitive data such as cookies or login information and potentially compromise the entire user account.

Cross-Site Scripting (XSS)
Digital threats for operators of critical infrastructures

SQL Injection

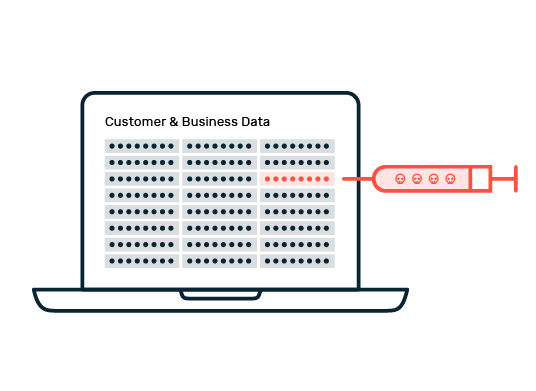
In an SQL injection attack, cybercriminals specifically exploit security vulnerabilities to inject manipulated commands or malicious code via input masks, for example. The attackers aim to manipulate the underlying database and gain unauthorized access to confidential information.

SQL Injection
Digital threats for operators of critical infrastructures

Zero-Day Exploits

Zero-day exploits are security gaps in software or hardware that are still unknown to the manufacturer and for which there are no patches yet. These vulnerabilities are exploited by attackers to compromise systems, often before the affected companies have even found out about the gap. Nevertheless, there are suitable solutions for taking appropriate countermeasures promptly until the necessary updates are available.

Digital threats for operators of critical infrastructures

Cross-Site Request Forgery (CSRF)

Attackers trick the user's browser into sending manipulated HTTP requests to a website or web application to trigger unwanted actions. This is done, for example, by sharing manipulated links or by visiting malicious websites, which in turn execute an HTTP request in the context of the existing user session.

Cross-Site Request Forgery (CSRF)
Digital threats for operators of critical infrastructures

OWASP Top 10

The OWASP Top 10 is a list of the ten most critical security risks for web applications, which is compiled and regularly updated by the Open Web Application Security Project (OWASP) Foundation. They serve as an important document for developers and security experts to find out about the most common and most dangerous security vulnerabilities in web applications.

Digital threats for operators of critical infrastructures

DDoS Attack

In a distributed denial of service (DDoS) attack, attackers direct artificial traffic to the IT infrastructures, web applications or online APIs of operators of critical infrastructures. As a result, the affected services are slowed down or fail completely. The problems continue until the attacker ends the attack or the affected organization takes appropriate countermeasures.

DDoS attacks
Sanctions

Fines and Liability for Non-Compliance

Operators of critical infrastructure are subject to particularly strict regulations on data protection and IT security. Violations of these regulations can have serious consequences. The General Data Protection Regulation (GDPR) provides for fines of up to 20 million euros or four percent of annual global turnover if critical infrastructure facilities violate the regulations.

The German Implementation Act for the NIS 2 Directive further tightens the sanctions. It provides for fines of up to 10 million euros or up to two percent of annual global turnover. These sanctions can be imposed for serious breaches of cybersecurity requirements.

Furthermore, NIS-2 explicitly obliges management levels to implement and maintain appropriate security measures. Failures in this area can result in personal liability risks for management bodies. The possible sanctions are not limited to financial aspects. There is also the possibility of criminal law consequences, which further increases the pressure on KRITIS operators and their management bodies to act. To minimize risks, critical infrastructure operators should establish robust security systems and continuously review their effectiveness.

Justitia

Fortify Your Digital Defenses With Myra

4 key areas – 1 outstanding technology

Icon radar

Security

Avoid data theft, system outages, and disrupted communications. Our robust defense system protects your critical processes with unwavering vigilance.

Icon Performance

Performance

Experience high-performance delivery of your content, even during traffic peaks. Maintain optimal performance and provide your users with a seamless experience.

Icon Compliance

Business Continuity

Myra ensures the utmost protection for your business by utilizing direct and geo-redundant connections to your infrastructure, without relying on external factors.

Icon Certificate Management

Compliance

Meet the requirements of IT security and data protection teams with ease. Myra is your trusted partner, offering unrivaled expertise in the strictest compliance regimes.

SUCCESS STORY

Federal Ministry of Health

Industry: Public sector
Employees:
> 500

The collaboration between Myra and coding. powerful. systems. CPS GmbH enables the Federal Ministry of Health to keep its TYPO3 website constantly highly available and performant. Even with high visitor numbers, the ministry's website is quickly and stably accessible.

Designed and engineered for highly regulated sectors

Certified Security from Myra: Compliance Without Compromise

  • ISO 27001 on the basis of IT-Grundschutz (BSI)

  • Payment Card Industry Data Security Standard (PCI DSS)

  • BSI C5 Type 2

  • KRITIS Proof according to § 8a para. 3 BSIG

  • Trusted Cloud Service

  • IDW PS 951 Type 2 (ISAE 3402)

  • Certification of data centers according to DIN EN 50600

  • VS-NfD

Certificate ISO 27001 BSI certified on the basis of IT-GrundschutzCertificate PCI DSSBSIG KRITIS qualified logoBSI C5 Testat Typ2Zertifikat Trusted CloudIDW WPS 951 Type 2 Certificatebrandeins best IT-security provider 2024 certificate

Do you have
questions?

Please contact us via contact form or call us at:
+49 89 414141 - 345.

All information on data processing can be found in our privacy policy.