New: AI Workspace – Secure AI for Organizations With Sensitive Data. Learn more.


At a
Glance
- 1. What Is a Credential Stuffing Attack?
- 2. How Does a Credential Stuffing Attack Work?
- 3. Why Do Attackers Use Bots for Credential Stuffing?
- 4. How Is Credential Stuffing Different from Brute Force and Password Spraying?
- 5. Which Industries and Companies Are Most at Risk?
- 6. What Are the Consequences of Credential Stuffing for Businesses?
- 7. What Is the Best Way to Stop Credential Stuffing Attacks?
- 8. Credential Stuffing Requires a Layered Defense





How Is Credential Stuffing Different from Brute Force and Password Spraying?
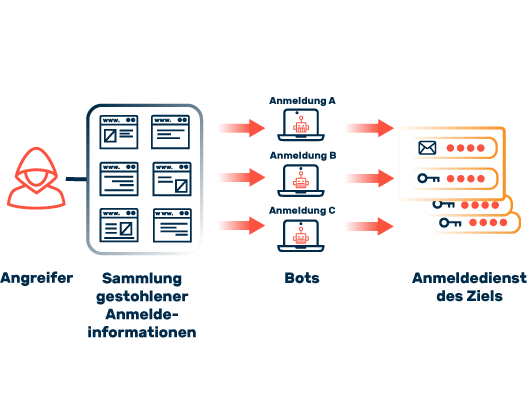
These three attack types are often confused, but they work very differently. The key difference: Brute force attacks guess credentials without context and usually fail against modern web applications with basic protections. A credential stuffing attack, however, can succeed – because even strong passwords don't help if users reuse them across services.
Basis
Real leaked credentials
Randomly generated passwords
List of common passwords
Target accounts
Many accounts in parallel
One or few accounts
Many accounts
Detectability
Hard to detect
Easy to detect
Medium
Success rate
Relatively high
Low against strong passwords
Medium
Prerequisite
Password reuse
Weak passwords
Common default passwords
Basis
Real leaked credentials
Target accounts
Many accounts in parallel
Detectability
Hard to detect
Success rate
Relatively high
Prerequisite
Password reuse


What Is the Best Way to Stop Credential Stuffing Attacks?
The best way to stop credential stuffing attacks is a layered defense combining technical and organizational controls. No single measure is enough – but the following building blocks work together to deliver reliable credential stuffing mitigation.
Multi-Factor Authentication (MFA): Multi-factor authentication is by far the strongest defense against most password-based attacks — a Microsoft analysis suggests MFA would have prevented 99.9% of account compromises.
Bot Management: Since these attacks are almost always automated, real-time bot management technology is often the best defense. Modern systems use behavioral analysis, machine learning, and device fingerprinting.
CAPTCHA and Adaptive Challenges: Adaptive CAPTCHAs – triggered only under suspicious conditions such as unusual login locations or rapid login attempts – improve security without hurting the user experience.
Device Fingerprinting: JavaScript can be used to collect information about user devices and create a unique "fingerprint" for each session, based on parameters such as operating system, language, browser, time zone, and user agent.
IP and Traffic Analysis: Correlating authentication traffic with proxy and IP intelligence, as well as known hosting provider IP ranges, helps identify highly distributed credential stuffing attacks.
Enforce password security: When assigning passwords, implement automated checks against known leaked passwords (e.g., HaveIBeenPwned), establish strong password policies, and encourage the use of password managers and passkeys.
Web Application Firewall: A modern WAF detects suspicious patterns in authentication traffic and blocks automated access attempts before they reach the login screen.


Would you like to learn more about our solutions, use cases, and best practices for defending against attacks? In our download section, you’ll find product sheets, fact sheets, white papers, and case studies.
FAQ on Credential Stuffing
In a credential stuffing attack, both username and password are already known — attackers simply test where they still work. In credential cracking, only the username is known, and the password is guessed using dictionaries or brute force.
About the author


Stefan Bordel
Senior Editor
About the author
Stefan Bordel has been working as Editor and Technical Writer at Myra Security since 2020. He is responsible for the strategic development and editorial management of all content formats – from website content and specialist publications to whitepapers, social media communication, and technical documentation. In this role, he combines solid expertise from IT journalism with in-depth technical understanding in the field of cybersecurity. As a long-time Linux enthusiast, he closely follows developments in the IT industry both professionally and personally.